 Tools
PortWatch
Every listening port, named and proven.
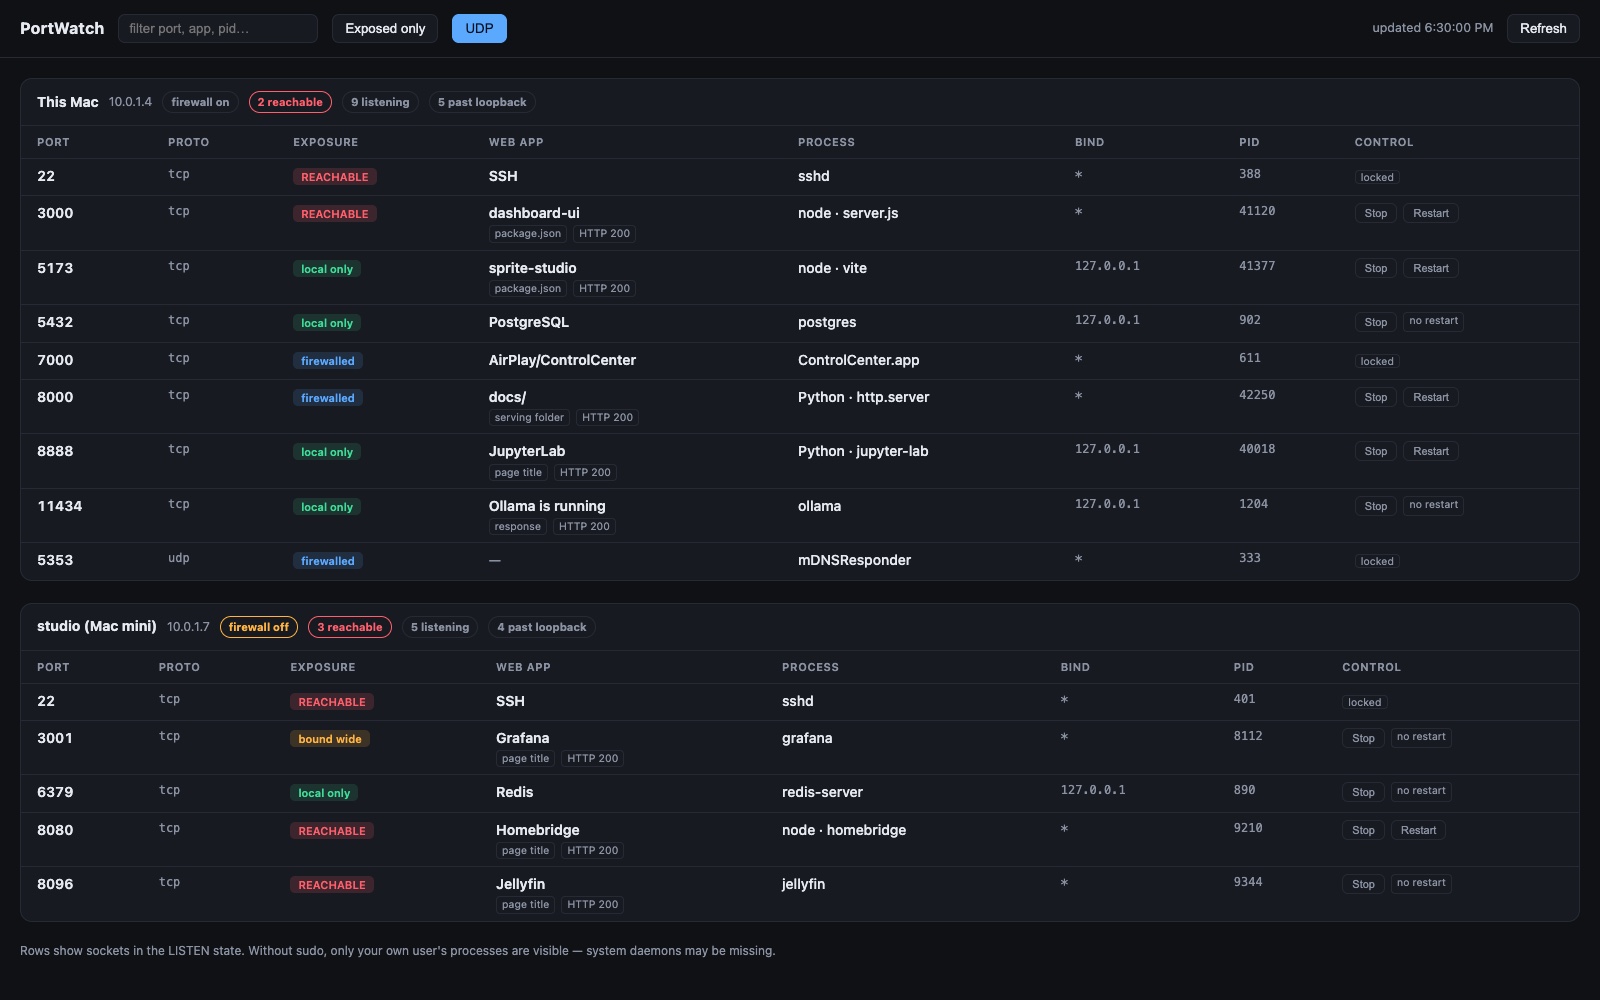
A macOS menu bar app that shows every listening port on every Mac you own, which app it belongs to, and whether the network can actually reach it. It doesn't trust a 0.0.0.0 bind; it opens a real connection and reports what answered.
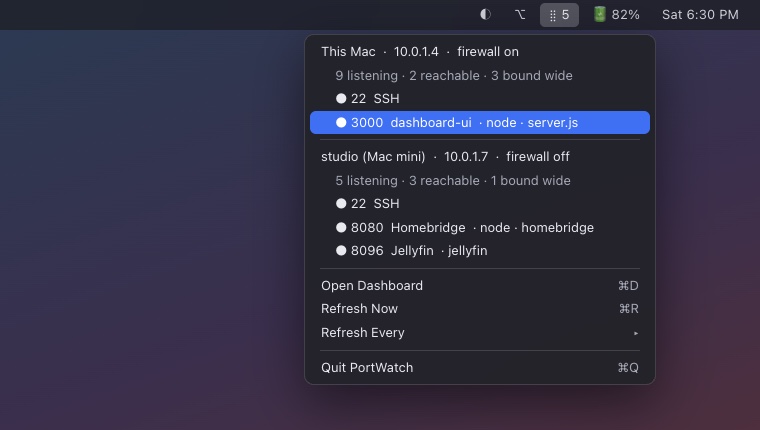
lsof stops at "bound to 0.0.0.0", which is a claim, not a fact. And on a dev machine, fifteen Python servers all report the same name; the port number tells you nothing about which project is which. PortWatch had to prove reachability and recover identity, on remote Macs too, without an agent installed anywhere.
Three Python files; the scanner and dashboard are stdlib only. One shell round trip per host gathers sockets, process table, firewall state, and IP, and the same probe string runs locally or over ssh. Ports get named by asking each server what it calls itself: page title, JSON body, package.json, serving folder. Then a second pass opens real TCP connections from outside, so REACHABLE means something answered. Stop and Restart come with guardrails: PID-reuse verification before any signal, server-side argv re-quoted through shlex, and a loopback-only dashboard with a per-run token against DNS rebinding.
In the menu bar every day. The glyph reads the count that matters: three ports answered from the LAN, or a checkmark for quiet. A full local scan takes about 250 ms, and the same table covers every Mac in the house.
Devlog
from the bench- Stop/Restart with PID-reuse guard; dashboard token + Host-header check
- Identify pass: ports name themselves via title, JSON, package.json, or serving folder
- Scanner, menu bar app, launchd installer; one probe round trip per host
One question, answered precisely: what can reach my machines? Small tool, real verification, guardrails on every part that can do harm. That's how I like to build.